Security and Operational Risks of Telegram Casino Integrations
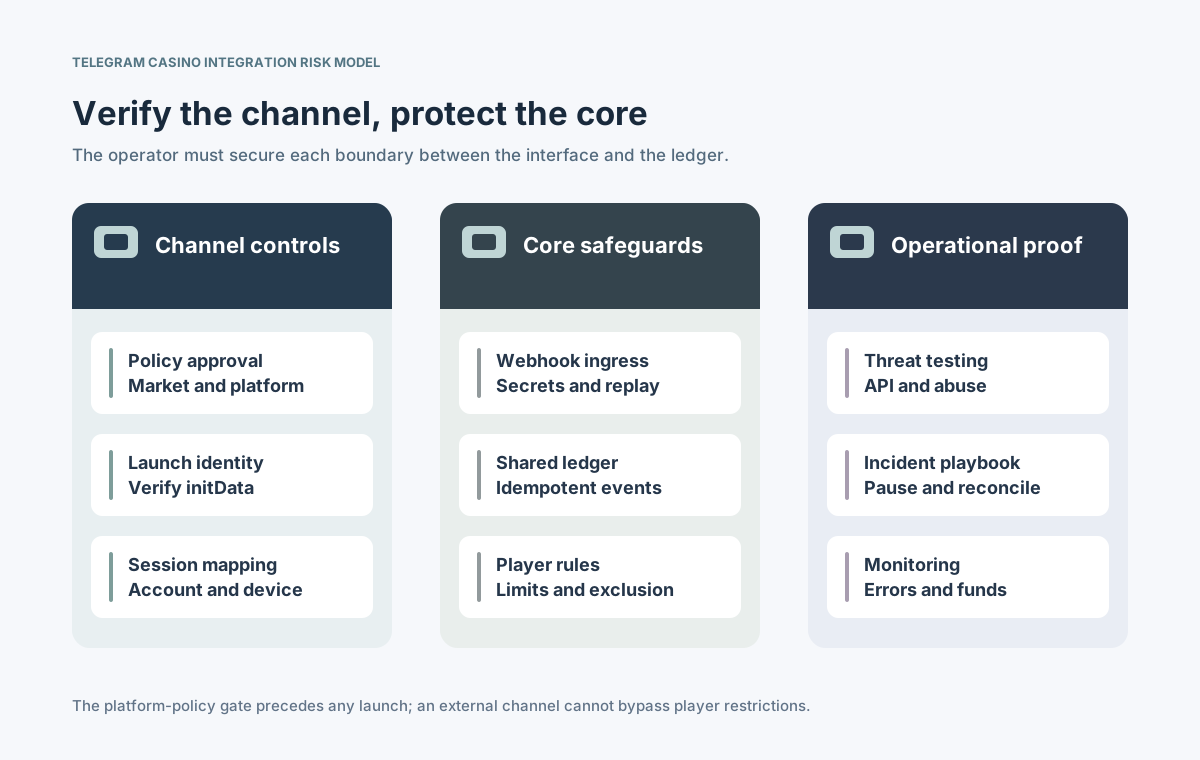
A casino bot or Mini App is a separate client for a gaming backend, not a separate source of financial truth. Its launch and operating risks begin even before authentication: the proposed service must comply with Telegram's developer terms and with every applicable gambling law and platform policy. If the use case cannot be confirmed as permitted, deployment remains on hold. Once this gate is resolved, engineering teams must validate signed launch data, establish their own sessions, protect webhooks, enforce player restrictions, reconcile shared-wallet transactions and plan for Telegram-specific outages. This article describes an architecture review and operational checklist, not a claim that real-money casino services are permitted on Telegram. [1] [2] [3] [4] [5] [6] [7]
Published
Telegram is an external channel; the operator retains responsibility for eligibility, identity, transactions and incident response.
On this page
Where do Telegram casino integration risks begin?
The first risk is feasibility, not code. Telegram Bot Platform Developer Terms require third-party applications to respect platform rules and applicable law and contain restrictions regarding regulated or questionable goods and services. The operator must obtain an affirmative, documented platform-policy and jurisdiction-specific decision for the exact product, brand, payment route and market before considering launch. [1] [6]
If the service is not permitted, do not deploy it, redirect restricted users to alternate gambling channels or reinterpret interface features as a workaround. For an allowed scenario, diagram where Telegram clients, bot infrastructure, the casino API, identity service and wallet exchange trust. A verified messenger identity alone is never proof of age, jurisdiction or right to gamble. [2] [5]
Which platform, legal and contract gates apply?
The review should distinguish Telegram's service and developer terms, the operator's local gambling authorisation, agreements with games and payment suppliers, and player-protection obligations. Telegram describes Mini Apps as third-party services and does not assume responsibility for their operation or payment disputes. These are distinct contracts and risk owners. [1] [7]
Gate
Decision before launch
Evidence owner
Telegram policy
Is this use case allowed?
Platform and legal
Gambling law
Are market and product authorised?
Regulatory counsel
Supplier terms
Are bot/Mini App channels covered?
Commercial legal
Player access
Can age, location and exclusions be enforced?
Player safety
Payments
Is the route lawful and contracted?
Finance and PSP
Data processing
Are notices, transfers and roles mapped?
Privacy lead
Record the actual policy version, reviewer, jurisdiction, approved scope, exceptions and revocation trigger. If any required permission is unknown, classify it HOLD. Telegram's rules may change, so recheck them before expansion and after material product changes. [1] [7]
How should Mini App identity and initData be validated?
Telegram's Mini App documentation explicitly warns that initDataUnsafe must not be trusted. Send raw initData to the backend and verify its integrity with Telegram's documented HMAC mechanism, or the documented third-party signature route when appropriate. Validate freshness, expected bot identity and user mapping before issuing a separate operator session. [2]
Verify the complete signed launch payload server-side using the correct bot-specific secret or public-key scheme.
Reject expired, malformed, duplicated or unexpected launch contexts under a documented replay policy.
Map a Telegram user identifier to a casino account only through an approved binding and recovery workflow.
Run independent KYC, age, location, session and responsible-gambling checks before any restricted action.
Never interpret a Telegram username, chat display name or client-supplied user object as a verified legal identity. Separate session establishment from account linking, record consent where required and protect account recovery against SIM, device and messenger-account changes. NIST provides a risk-based identity framework, not a gambling licence. [2] [5]
What session architecture keeps channels isolated?
The Mini App launch assertion should create a short-lived, audience-bound operator session only after verification. The gaming backend owns the actual player identity, authorisation decisions, step-up controls, revocation and limits. A web session and a Telegram session may reference one account, but each has its own device, token lifecycle and anomaly record. [2] [4] [5]
Verify Telegram launch context, then establish an operator-issued session for an eligible account.
Bind actions to player, tenant, market, device/session scope and current restriction state.
Enforce authorisation on every server-side wallet, game and account endpoint.
Revoke compromised sessions and propagate exclusion or limit changes to all channels.
⊕View largerThe Telegram client is untrusted; the operator's backend controls session, money and player restrictions.
Do not place long-lived gaming credentials, bot tokens or provider secrets in Mini App JavaScript, chat messages or URL parameters. Use narrow permissions, token rotation, secure cookie or equivalent session safeguards and server-side rate controls. [4] [5]
How can bot webhooks and APIs fail safely?
Telegram's Bot API delivers webhook updates over HTTPS and may retry unsuccessful deliveries. Its setWebhook method supports a secret_token returned in the X-Telegram-Bot-Api-Secret-Token header. Authenticate incoming events, restrict endpoints and handle repeated or out-of-order updates without duplicating business actions. [3]
Ingress risk
Required defence
Proof to collect
Forged callback
Webhook secret and validation
Invalid token rejected
Repeated update
Stable idempotency key
One business outcome
Out-of-order event
State-machine validation
Safe final state
Bot token exposure
Secret vault and rotation
Rotation rehearsal
Excessive traffic
Rate and queue limits
Backpressure test
A response acknowledging an update is not confirmation that a deposit, withdrawal or wager settled. Separate the messaging transport acknowledgement from the operator's authoritative transaction result, and keep audit traces without storing sensitive message content unnecessarily. [3] [4]
How do shared wallets avoid inconsistent transactions?
A player may switch from a website to Telegram mid-session. Both entry points must use the same authoritative ledger and reservation rules. Bot message order is not accounting order; retries and double taps must not create a second debit or bonus claim. Keep wallet transaction IDs independent of Telegram update IDs and payment-provider callbacks. [3] [4]
Deduplicate each financial command using a stable operator-generated idempotency key.
Serialize or reserve funds for overlapping bets and withdrawals across channels.
Use authoritative provider settlement status, never an animated success state in chat.
Test delayed game callbacks, partial outages, duplicate confirmations and compensation.
Telegram's Mini App terms explain that payment providers and third-party operators manage transaction disputes; Telegram does not settle them. Define support ownership and reconciliation separately from any Telegram invoice or payment UI. Do not assume Telegram's general payment features are appropriate or permitted for gambling. [7]
What fraud, privacy and player-protection risks increase?
A messenger entry point can increase phishing, impersonation, referral abuse, unsolicited notifications and mistaken account linking. Apply bot identity verification, explicit consent and channel-specific monitoring while retaining the operator's authoritative exclusion, age, AML and eligibility decisions. OWASP highlights API authentication and object-level authorisation risks. [1] [4] [6]
Risk
Control owner
Validation
Fake bot or link
Brand security
Verified entry path
Account misbinding
Identity team
Recovery challenge
Referral manipulation
Fraud operations
Abuse thresholds
Exclusion bypass
Player safety
Cross-channel block
Private data in chat
Privacy and support
Redaction review
Minimize chat content containing balances, identity documents or recovery data. Never request Telegram passwords or one-time codes; Telegram's developer terms prohibit such deceptive behaviour. Review notification frequency, opt-outs and market-specific marketing permissions before sending messages. [1]
What availability and observability problems are different?
Telegram is an external dependency outside the casino operator's release control. Bot API failures, unavailable WebView clients, delayed webhook updates or client-version differences may interrupt the interface while the core platform remains healthy. Design useful synthetic checks and monitor both transports and real account outcomes. [2] [3]
Define a safe unavailable state with clear support directions and no invented success confirmation.
Apply backpressure and bounded retries; test dependency recovery without lost or duplicated actions.
A green bot uptime chart is not proof that balances and player restrictions remain correct. Tag incidents by market, brand, channel and correlation ID while avoiding unnecessary personal data in logs. [3] [4]
How should teams respond to compromised bots or outages?
Incident ownership must be explicit: platform engineers contain webhook and token exposure; security investigates identity and abuse; finance reconciles funds; player-safety teams verify restrictions; compliance evaluates legal and platform notifications. The operator owns customer communication and operational recovery. [1] [6] [7]
Pause risky Telegram actions using a controlled server-side feature flag without invalidating ledgers.
Rotate compromised bot/webhook credentials and revoke affected operator sessions.
Reconcile every pending financial event against the authoritative ledger and provider records.
Verify account links, exclusion status and player communication before restoring traffic.
Review root causes, evidence gaps, runbook quality and control-owner sign-offs.
Test a full bot-token compromise and a multi-hour webhook outage. Record detection, containment, financial reconciliation, privacy review and authorisation to restart. If the platform-policy approval is withdrawn, keep the service closed.
Which tests belong in a secure Telegram integration gate?
The final approval record must first confirm that the exact service is permitted by Telegram and applicable gambling regulation. Only then should security, product, finance and operations approve a specific software version, market, bot identity and integrations. No technical test can waive a policy prohibition. [1] [6]
Policy and legal: current platform terms, licence, market, supplier and payment permissions confirmed.
Identity: signed initData, freshness, session binding, step-up, account recovery and revocation tested.
Webhooks: secret verification, retries, ordering, load and credential rotation validated.
Money and safety: shared ledger, idempotency, limits, exclusion and refunds reconciled.
Operations: monitoring, support ownership, dependency outage, incident and rollback drills signed.
Archive the decision, source versions, test results, release hashes, remaining risks and named approvers. Rerun the gate when Telegram policies, game permissions, bot credentials, supported clients or the casino backend change. A launch remains HOLD until every blocking item is resolved.